Betalright Privacy: Anjouan Account Data Request
Harriet Cole revised this data-request guide on 9 November 2026 with safe document handling and focused requests for British account holders.
Betalright Privacy: Data Behind the Account
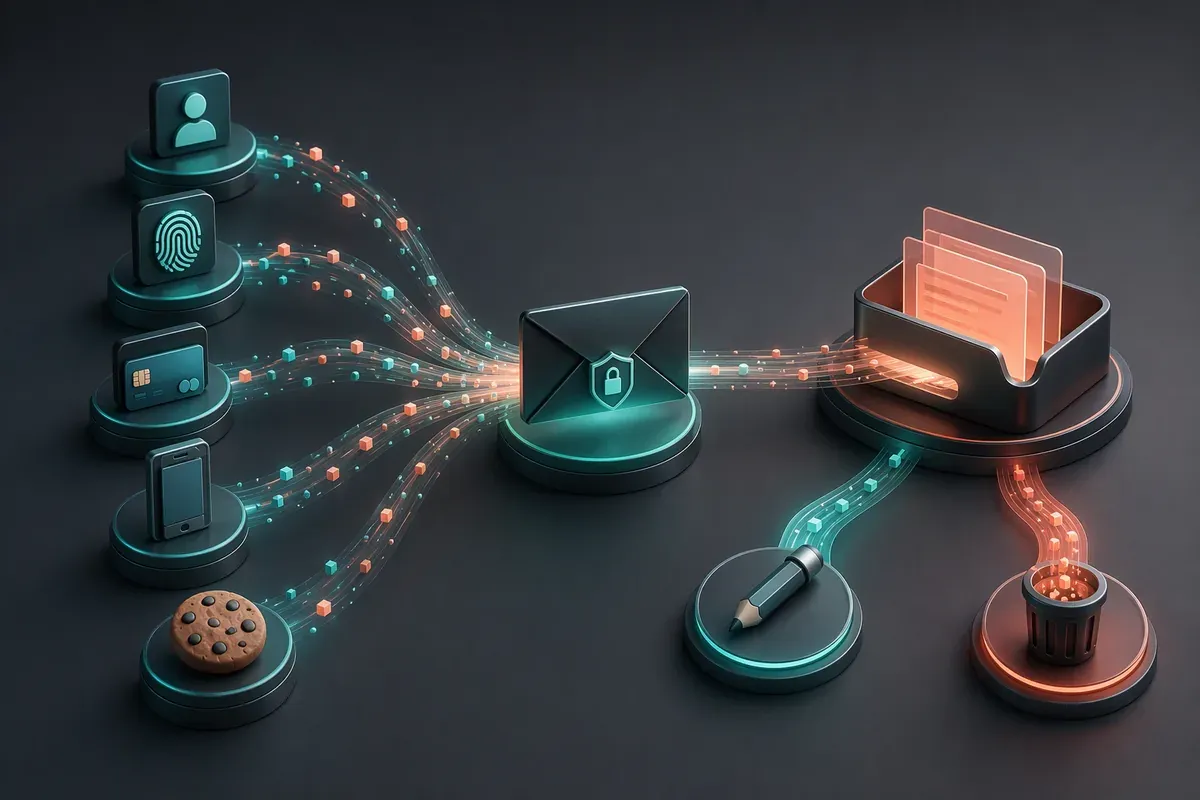
A casino account can involve registration details, identity and address documents, payment-ownership records, transaction history, game activity, support conversations, device information and cookies. The operator’s current privacy notice supplies the legal purposes, retention periods and recipient details.
This independent guide helps you organise a request; it is not the operator’s legal notice and does not receive your account data. British and other data-protection rights can depend on the controller, jurisdiction and applicable exceptions, so ask which legal entity handles the account.
Never send passwords, full card security codes, private keys, seed phrases or one-time authentication codes with a privacy request. Use the authorised account route for identity documents and mask unrelated information only as permitted.
Start with the controller
Use the genuine privacy notice and licence record to identify the legal entity and contact route. Keep the notice version and request date with your ticket.
Start with one purpose
Ask for access, correction, deletion or another specific outcome rather than sending a broad demand for every possible action. A focused request is easier to route and answer.
Anjouan Account Data Request
Account, KYC and Payment Data
Registration data can include name, email, phone, date of birth, address and currency choice. Verification can add identity, address and payment-ownership documents. Payment history can connect those records to method, amount, status and transaction references.
Review what is actually requested before submitting a file. Clear images and matching details reduce avoidable rejections, while unrelated records increase unnecessary exposure. Follow the authorised masking instructions and retain the upload date and document category.
For a payment-specific access or correction request, identify the transaction without sending a complete statement. The provider can explain its own processing record, while the casino can explain the account entry.
| Data category | Examples | Safer request focus |
|---|---|---|
| Registration | Contact, identity fields and currency | Access or correct a named field |
| Verification | Identity, address and ownership documents | Submission status and retention explanation |
| Payments | Method, amount and transaction status | Records for one specified event |
| Gameplay | Title, round and account history | Access to a defined period or round |
| Support | Messages, tickets and uploads | One conversation or case reference |
A data-minimisation habit
Provide the requested field or document rather than every available record. Crop unrelated transactions where permitted and keep required identifying details readable.
A payment-record request
Name the method, amount and timestamp, then ask which stored ownership or status records relate to that event. Do not attach private wallet credentials.
Device, Cookie and Marketing Preferences
Device and log data can support security, troubleshooting and account access. Cookie and similar technologies can remember preferences, maintain sessions or measure site use. The current notice and consent controls explain which categories are used and how to change them.
Use genuine account or browser controls to review optional permissions. Blocking necessary session cookies can affect login, while optional marketing preferences should be changed through the stated route. Deleting an icon does not remove server-side account records.
Promotional messages can be stopped without abandoning a privacy or payment request. Ask which communication categories are affected and retain the confirmation. Safer-play restrictions should not be weakened to preserve marketing.
A device-data question
Ask which security or access records relate to a named login event, providing the time and device type but no authentication secret.
A marketing-preference question
Ask for optional promotional messages to stop and for written confirmation of the channels or categories covered by the request.
Access, Correction, Deletion and Retention
An access request asks what data is held; a correction request identifies an inaccurate field; a deletion request asks what can be erased. These are different outcomes and can require different identity checks. State the one you need first.
Retention obligations and legal exceptions can mean that not every record is deleted immediately. Ask which category is retained, the applicable reason and the expected period where the controller can provide it. Account closure and data deletion are not necessarily the same event.
If you are asking from Great Britain, explain your location and ask which rights process applies to the named controller. Do not assume that an offshore jurisdiction eliminates every privacy obligation or that every request has an identical outcome.
When a request is refused
Ask for the specific reason, the record category and any available review or complaint route. Keep the original request and response together.
When security is a concern
Use the formal recovery and account-protection process first. A privacy request should never require you to disclose the credentials it is meant to protect.
Sending a Request Without Creating New Exposure
Use the genuine privacy or account-support destination and verify the address before attaching anything. Send only the requested material, and keep a personal log of the date, purpose and ticket reference. Do not post identity or payment documents in public channels.
A safe screenshot shows the relevant field or status while excluding unrelated personal and financial details. Never alter a required verification field. If the controller needs an unedited document, use the authorised upload route rather than ordinary chat.
This independent website does not need your private records to correct its own content. For an editorial correction, provide the page and wording only.
For family or authorised representatives
Ask which authority and identity process is required before discussing another person’s account. Do not share someone else’s credentials or documents without the required authorisation.
After the request
Store the confirmation securely and review account sessions or marketing preferences if relevant. Deletion or correction does not remove the need to protect the registered inbox.